An inadequately isolated PHP process or a vulnerability in a third-party plugin is often enough to compromise the integrity of an entire hosting environment. System administrators are then faced with the complex task of analyzing and remedying the resulting damage at the server level. However, the assumption that a system can be completely cleaned up using standard tools usually proves to be a fallacy in practice. Once malicious code reaches deep system levels or structurally damages database tables, conventional recovery measures inevitably reach their architectural limits. This article examines the structural vulnerabilities of modern content management systems. It provides a detailed analysis of the ways in which malicious code infiltrates the infrastructure and explains why a complete restoration of the original state at the code and database levels can hardly be guaranteed from a technical standpoint following a massive compromise.
Anatomy of a Server-Side Breach and Initial Damage Control
When attackers exploit a vulnerability in a theme or plugin, initial access almost always occurs via the web server. NGINX or Apache executes the manipulated HTTP request, after which the PHP-FPM process runs the malicious routine with the privileges of the respective system user. This allows the immediate deployment of initial dropper scripts in the server’s file system. Administrators often do not notice the incident until later, due to load spikes, unusual outbound traffic, or the blacklisting of the assigned IP address.
If a system is compromised in this way, immediate isolation measures must be implemented at the network level. If a WordPress hacked Once this has occurred, the first step is to consistently block external access and prevent any outgoing connections. Simply deactivating the affected plugins via the Command Line Interface (WP-CLI) is no longer sufficient at this stage of escalation. By this point, the malicious code has usually already spread far beyond the initial infection vector within the system.
„A purely file-based cleanup ignores the persistence that modern malware embeds deep within the server's database structures and memory.“
The strict isolation of the affected virtual host at the CloudLinux level reliably prevents the infection from spreading to neighboring instances. However, the specific container itself remains completely compromised. An in-depth analysis of the NGINX access logs and the PHP error logs is absolutely necessary to determine the exact time the infection began. Only through this preliminary forensic work can it be determined whether an undamaged backup from before the incident still exists on the storage systems.
Persistence Mechanisms: Why Malicious Code Survives System Restarts
Modern malware architectures are no longer limited to simple script injections into index.php or wp-config.php. They use highly complex persistence mechanisms to ensure long-term access to the web server and evade detection. A popular technique is the targeted modification of legitimate core files using Base64-encoded strings, which are only decrypted in RAM at runtime. This systematically circumvents traditional signature-based virus scans, as the actual malicious code remains heavily obfuscated on the hard drive.
Another major vulnerability is the manipulation of server-side cron jobs by automated scripts. Attackers write specific instructions into the web user’s crontab that regenerate hidden backdoors at regular intervals. Even if an administrator manually deletes the obvious malware files, the cron job ensures an immediate, automatic reinfection. This leads to a cyclical game of cat-and-mouse that ties up valuable server resources and severely hinders operational remediation.
At the database level, attackers particularly often embed their payloads in the `wp_options` table. Autoload entries are specifically exploited to load malicious PHP code directly from the database into the execution context every time a page is loaded. Since these entries are often hidden within serialized data structures, a simple search-and-replace operation at the SQL level inevitably results in the destruction of the data array. This immediately causes the functional integrity of the entire web application to collapse.
Structural Destruction: The Analytical Limits of Forensic Reconstruction
The expectation that a web instance can be reliably restored to its original state after a comprehensive infection ignores the fundamental architecture of the system. Once malware systematically alters file permissions at the operating system level or overwrites core components, it becomes virtually impossible to algorithmically reconstruct the clean initial state. Attempts to repair such corrupted structures step by step almost always result in inconsistent file fragments.
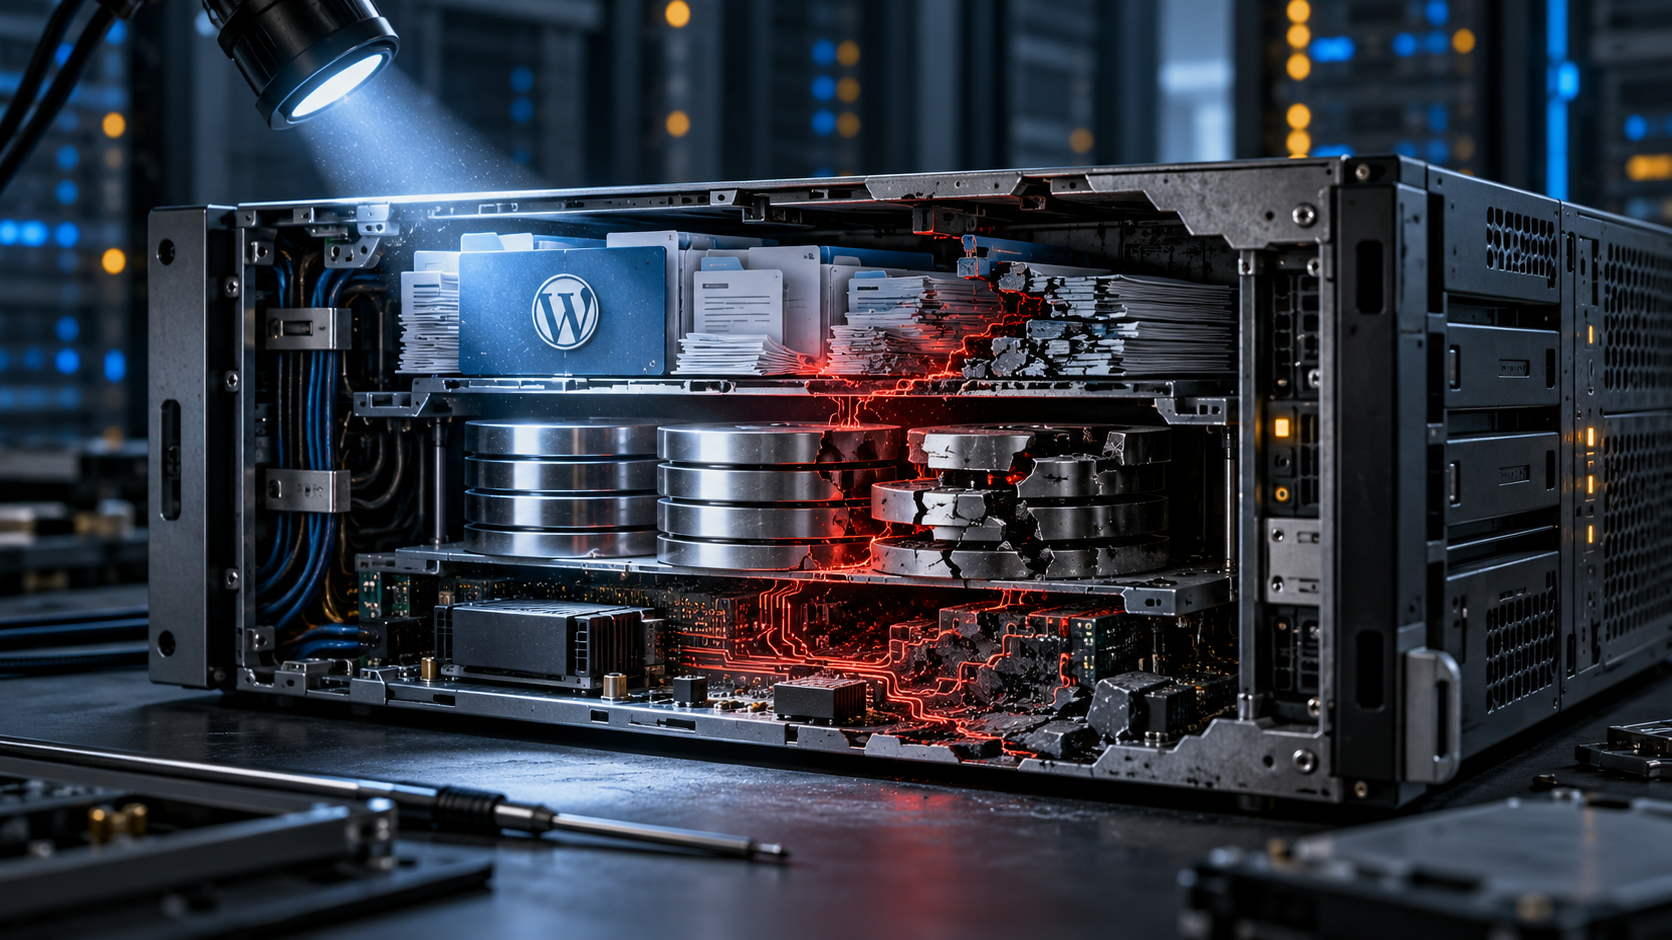
Upon closer analysis, this structural destruction usually manifests itself across multiple levels of the infrastructure. During forensic analysis, system administrators typically encounter the following patterns of irreparable damage:
- Corruption of serialized arrays: Malware scripts alter length specifications in serialized PHP objects within the database, resulting in the records becoming permanently unreadable and leading to their loss.
- Cascading authorization errors: Recursively setting incorrect permissions (such as CHMOD 777) on entire directory trees undermines Linux's finely tuned security model.
- Modifying Compiled Assets: Compromised build processes in custom themes inject malicious code directly into minified JavaScript files, whose clean source code isn't even available on the web server.
- Overwritten system binaries: In severe cases, the malware modifies system tools at the operating system level, meaning the server's root environment must be considered compromised.
The situation is particularly critical when the infection has profoundly altered the table structures of the MariaDB database. Attackers often delete existing indexes or change data types in order to create their own tables for external C2 (Command and Control) communication. Restoring the database to the exact schema of the original installation requires an enormous amount of manual effort that is prone to errors. In many cases, hidden triggers remain undetected in the database and continue to execute malicious code during regular operations.
Impact on Web Hosting Infrastructure and Caching Topologies
A serious server-side compromise by no means affects only the isolated content management system; rather, it often impacts the entire performance architecture. Malicious code typically generates a massive number of faulty database queries or manipulated external HTTP requests. This immediately maxes out the available PHP-FPM workers and permanently blocks the NGINX web server. Under high-load conditions, this triggers a denial-of-service condition that forces even completely unrelated projects on the same host offline.
Modern acceleration technologies further complicate error diagnosis in such scenarios. A FastCGI cache at the NGINX level stores the generated HTML pages directly in RAM or on high-performance NVMe SSDs. When malware injects redirects to external phishing sites, these malicious headers are captured by the cache and delivered statically at lightning speed. The actual PHP application is completely bypassed in the process, which makes identifying the source of the error extremely difficult.
When evaluating the necessary recovery measures, administrators must clearly distinguish between different escalation levels. The choice of analysis method plays a decisive role in determining the system's long-term stability.

In practice, attempts to simply patch a heavily infected environment almost always fail due to the restrictions of complex system environments. If deep-rooted rootkits have been installed, even the most meticulous cleanup by Webroot no longer provides any real security. While isolation via container technologies can prevent the infection from spreading to other users, it does not protect the affected tenant from the complete destruction of its own database.
Strategies for a Structured Rebuild Following a Total Loss
If system integrity has been irrevocably compromised, the administrative focus must be shifted from repair to secure data extraction. The technical goal is no longer to restore the old environment to a working state, but solely to recover the raw user data from the database. The virtual server on which the security incident occurred must be declared compromised and completely formatted in the medium term. Simply restoring a backup to the same web space—which may still be compromised—poses an incalculable risk.
The extraction process requires a strict and uncompromising separation of executable code and static data. All PHP files—whether core files, themes, or installed plugins—must be discarded without exception. Instead, administrators download verified, cryptographically signed original files from the official repositories. This radical approach guarantees that absolutely no modified scripts are transferred to the newly provisioned environment.
Cleaning up the exported database dump then requires the use of precise text-processing tools. Malicious code patterns are extracted from the affected tables and deleted using regular expressions at the command-line level. Extreme administrative caution is required here to avoid accidentally corrupting the UTF-8 encoding and the relational structures of the tables. After successful manual cleanup, the cleaned-up SQL dump is imported into a freshly set up MariaDB instance.
Finally, all database passwords and cryptographic salts in the central configuration file must be regenerated. The old, isolated environment will not be permanently shut down until the DNS record successfully points to the new, hardened server. This drastic architectural change is the only technically sound method to absolutely rule out any persistence of the malware.
Hardware-based hardening and server-side prevention
After a successful system rebuild, the hosting architecture must be proactively hardened against future attacks. Modern hardware components play a surprisingly crucial role in the efficiency of server-side security tools. A server with the latest PCIe 5.0 NVMe storage interface enables in-depth forensic scans and file integrity monitoring to be performed in a fraction of the usual time.
At the software level, the consistent implementation of live-patching concepts such as KernelCare is essential in today’s professional environment. These technologies enable administrators to apply critical security updates directly to the running Linux kernel without requiring an error-prone server reboot. Scheduled downtime for maintenance windows is completely eliminated, allowing newly discovered vulnerabilities in the operating system to be patched immediately upon discovery.
In addition, a modern Web Application Firewall (WAF) must be integrated directly at the reverse proxy level. Specific filter rules reliably block malicious requests, such as SQL injections, at the network level before they can even reach the PHP interpreter. When intelligently combined with proactive malware protection, this creates a robust, multi-layered line of defense for the entire infrastructure.